Security
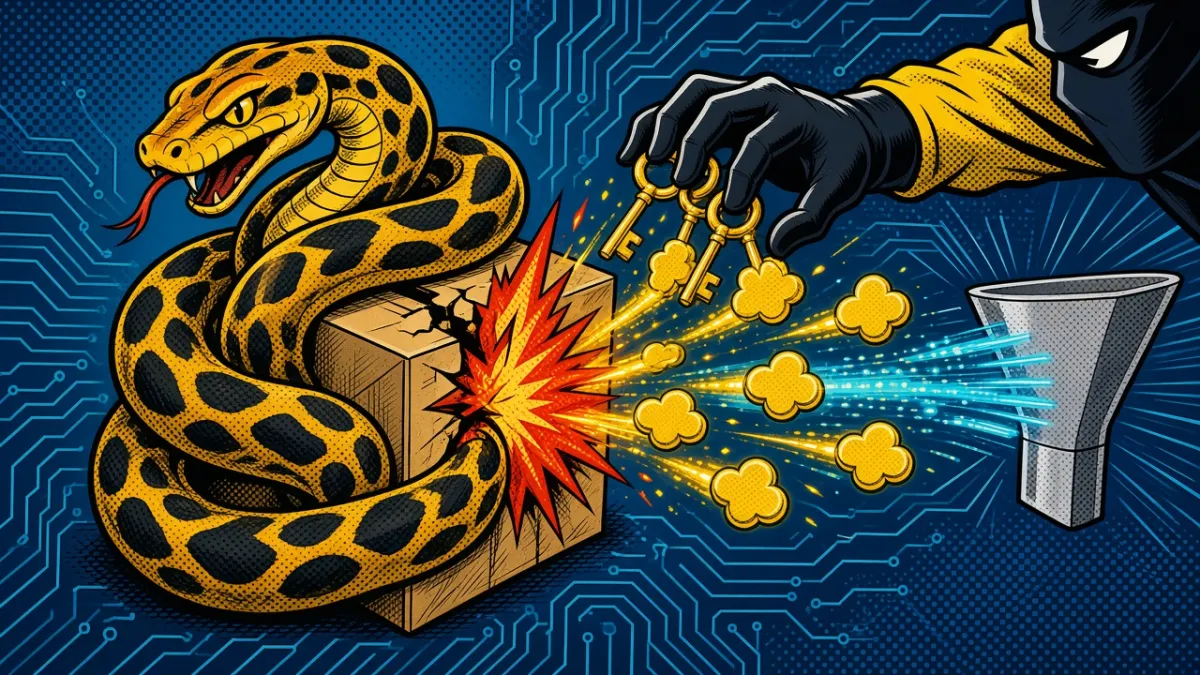
wfx-loot: hijacked GitHub accounts probed 61,764 repos and ran a CI secret stealer in 1,800+. What to check
Since November 10, an attacker using 4,837 compromised GitHub accounts has been slipping a self-deleting credential stealer into GitHub Actions workflows, then planting AWS and Azure backdoors that survive secret rotation. If you maintain repositories, here is how to tell whether it ran on yours.